- Publish a direct case workflow whose attributes match the fields the sender will post.
- Generate the workflow’s webhook URL in the dashboard.
- Point the external system at that URL. Each POST creates a case and runs the workflow.
Generate the webhook URL
- Open the direct case workflow in the dashboard and make sure it’s published.
- Open the Case Configuration tab, expand Case Sources, and click Incoming Webhook.
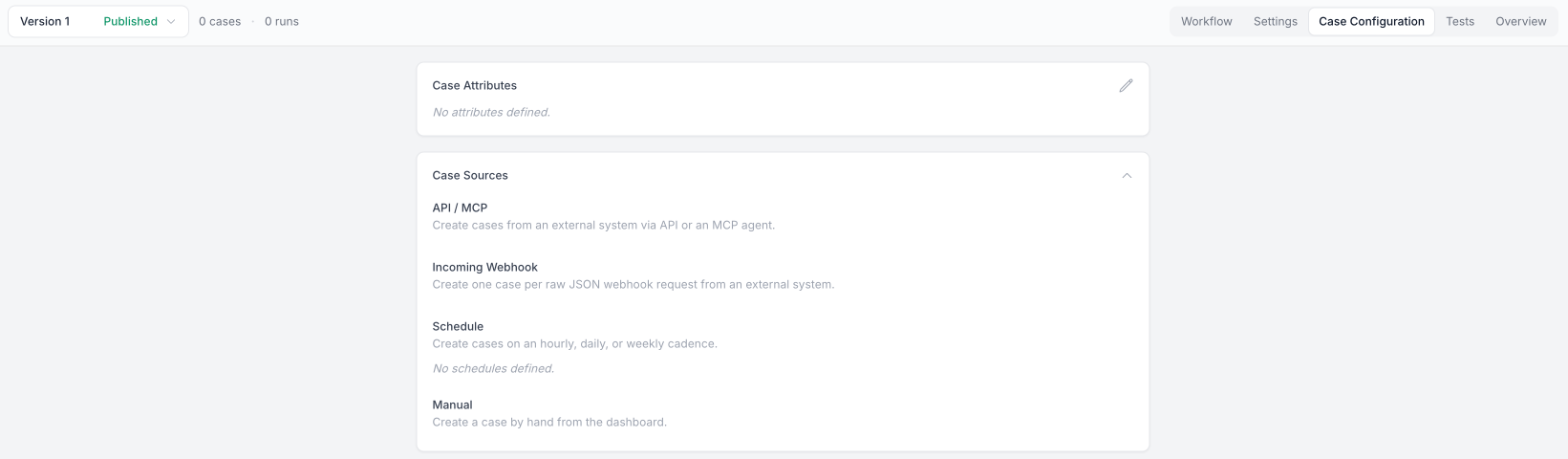
Incoming Webhook in the workflow's Case Sources.
- Click Generate webhook URL and copy the URL. The dialog also shows a ready-to-run curl example.
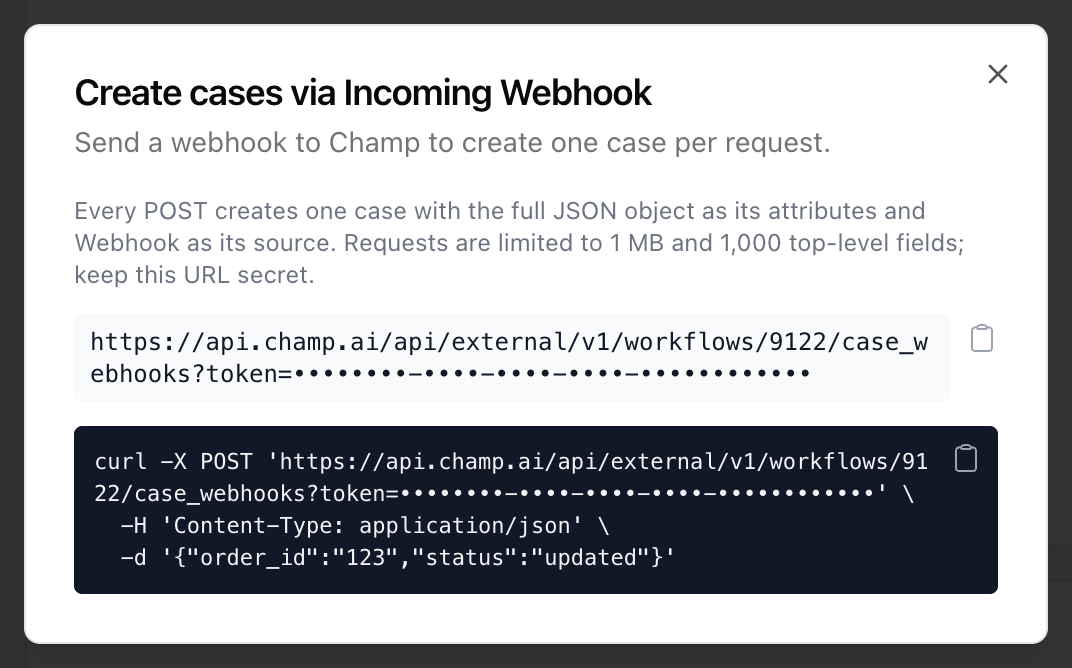
The generated webhook URL. The token is masked here.
token is not an API token. It’s a separate secret generated for
this workflow only. It can create cases on this workflow and nothing else: it can’t read or update cases, and it
doesn’t work for any other workflow or endpoint. Because it travels in the URL, the sender doesn’t need to set an
Authorization header, and any header it does send is ignored.
Send a webhook
POST any JSON object to the URL. NoAuthorization header is needed.
201 Created as soon as the case exists. The workflow runs asynchronously, so the response
doesn’t wait for it:
- Start in the
Openstatus, like every new case. - Are
livecases. There is no test mode on this endpoint; use the cases API with"mode": "test"for staging traffic. - Get a timestamped subject such as
Claims Intake via Webhook - 2026-10-15 17:04:12 UTC. - Show Webhook as their source in the dashboard.
Every request creates a new case, including retries of the same event. If your sender retries on timeouts,
include a stable event ID in the payload so the workflow can recognize duplicates.
Matching the workflow’s attributes
The payload is validated against the workflow’s case attributes before the case is created:- Every required (non-nullable) attribute must be present.
- Values for declared attributes must match their types.
- Keys the workflow doesn’t declare are kept as extra attributes. On workflows marked as handling sensitive data, undeclared keys are rejected instead, so that nothing is stored without its sensitivity setting.
422 and no case is created. Each entry in validation_errors points to
the offending field with a JSON Pointer:
Pattern: send a notification, let the workflow fetch the details
You don’t have to put everything in the webhook. A common setup is to send a small notification, such as an event ID and some metadata, and let the workflow decide what to do with it:- The external system sends a webhook with the item’s ID and the details needed to decide whether it’s in scope.
- The workflow checks those details. If the item is out of scope, it closes the case without accessing anything else.
- If it is in scope, the workflow calls the source system’s API through a REST API integration to download only the files or records it needs.
Following up on a case
The webhook response only returns the case ID. To follow the case after that:- Subscribe to webhook events to be notified when the case is closed or errors.
- Fetch the case with the cases API using an API token.
Limits
To send files larger than this, send a reference to them (an ID or URL) and have the workflow download them, as in
the pattern above.
Errors
Errors return a JSON body with an
error message.